Munitor: shared delivery tooling
Shared CI/CD tooling for reusable build, verification and release contracts across repositories.
active
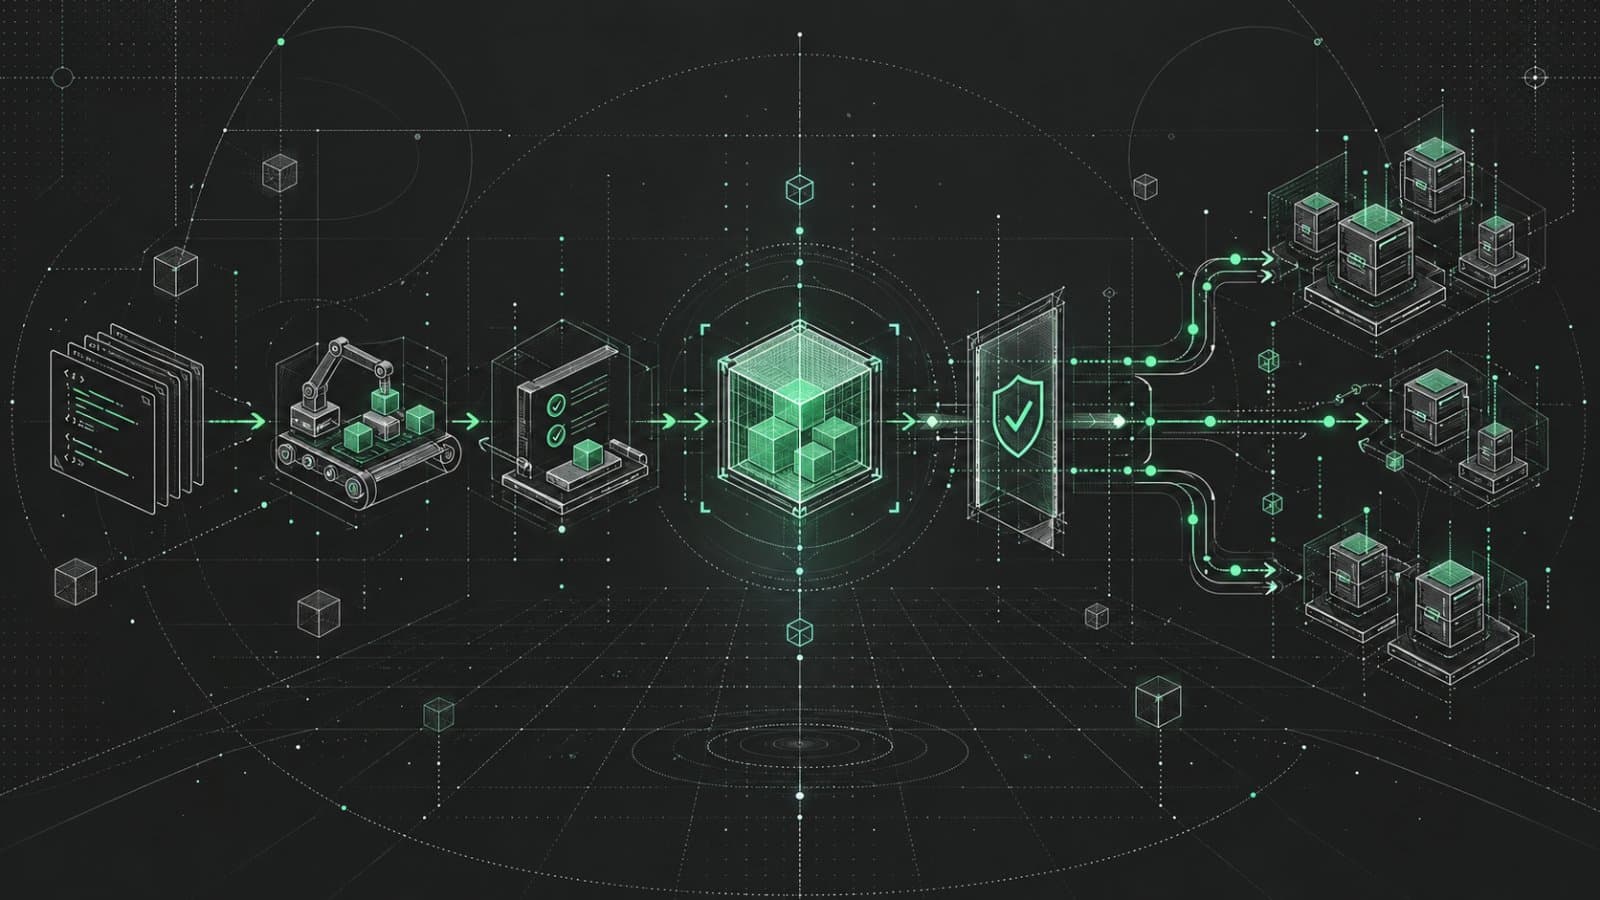
A delivery pipeline is part of a product’s architecture. It decides which source becomes an artifact, which checks apply and which environment receives the result. Munitor makes that contract reusable across repositories while leaving each application’s needs explicit.
CTO to Human: a shared delivery system
Repositories declare their pipeline requirements in .munitor.yml; a small CircleCI entry point invokes the shared orb. That creates one place to improve common delivery behavior without copying a pipeline into every project.
Centralization also concentrates responsibility. A shared pipeline change can affect many consumers, so the version adopted by an application is a meaningful dependency. The website uses this delivery model to build artifacts and update its GitOps deployment state.
Engineer to Engineer: configuration becomes a workflow
Munitor uses CircleCI dynamic configuration to select and generate pipeline templates. The public documentation covers Java web applications, Node applications, deployment-repository validation, infrastructure and SDK distribution. Branches and environments determine which workflow runs; production promotion is an explicit merge/release operation.
The documented release-integrity contract reserves a version tag atomically, associates it with the built source commit and prevents a differently built image from taking over the same version. GitOps write-back and GitHub release creation follow the built artifact. Those controls matter only when the consumer’s branch protections and earlier quality gates are configured correctly; a production fast path is not independent proof of review.
The Munitor repository and published orb document the delivery contract. This journal will make consumer integration and release boundaries visible rather than treating CI/CD as an unexplained final step.